Comparison Articles
All GeekWala articles in the Comparison category.
Software Composition Analysis Tools (2026)
Software composition analysis buyers evaluate a shortlist, not a single product. Here's a neutral, sourced comparison of 10 SCA tools — vulnerability detection, license compliance, and reachability — including where GeekWala fits and where it doesn't.
GitHub Code Security Pricing Explained
GitHub split Advanced Security into two per-committer SKUs. Here's what Code Security and Secret Protection actually cost at real team sizes, and how GeekWala's flat pricing compares for dependency scanning specifically.
Trivy vs Grype: Open-Source Scanner Comparison
Trivy (Aqua Security) and Grype (Anchore) are the two most-adopted open-source vulnerability scanners for containers and dependencies. Here's how they actually differ — no vendor picked.
Snyk Pricing Explained: What It Costs vs GeekWala
Snyk's pricing page lists four tiers and a per-developer model that gets expensive fast. Here's what Snyk actually costs at real team sizes, the free-tier limit teams hit first, and how GeekWala's flat pricing compares.
Snyk vs Dependabot vs Trivy: SCA Compared
We put Snyk, Dependabot, and Trivy through the same 10-point checklist without a vendor holding the pen. One wins on breadth, one wins on cost, one wins on zero setup — none wins everything.
Mend vs Flat-Rate EPSS + KEV Scanning
Mend bundles SCA, container, and license-compliance scanning with per-developer, contact-sales pricing built for large security teams. GeekWala is flat-rate dependency scanning with EPSS and CISA KEV on every finding. Here's an honest, feature-by-feature comparison.
OSV-Scanner vs EPSS Prioritization
OSV-Scanner and GeekWala read the same OSV.dev data, but only one of them scores exploitation probability. Here's how EPSS and CISA KEV change what a CLI table can't show you.
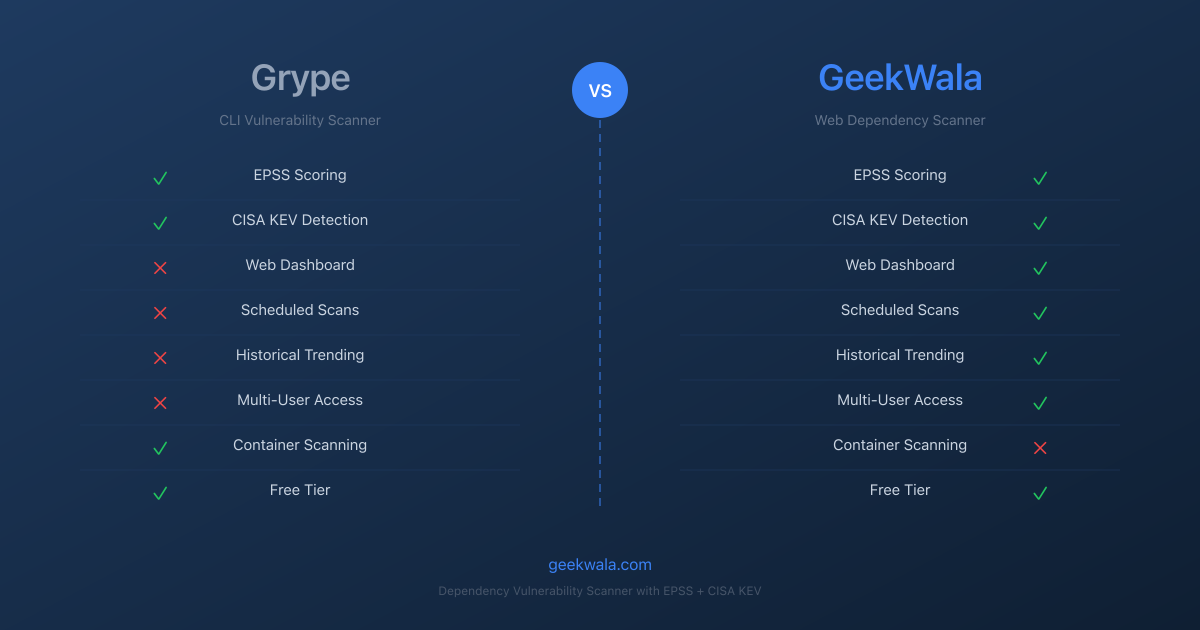
GeekWala vs Grype: Beyond CLI Scanning
Grype is one of the best CLI-based vulnerability scanners available, with genuine EPSS and CISA KEV support built in. But it's CLI-only. GeekWala serves teams that need a web UI, project history, and scheduled re-scans — not just CI/CD engineers who are comfortable with JSON output.
Dependabot PR Automation vs EPSS Triage
Dependabot automates PRs labelled by CVSS severity, with an EPSS score per alert. GeekWala adds CISA KEV confirmed-exploitation status as a first-class field and ranks KEV entries first. Here's how the two tools' triage signals actually differ, and how to use both together.
GeekWala vs Socket: CVE vs Behavioral Analysis
Socket.dev detects malicious packages through behavioral analysis. GeekWala prioritizes known vulnerabilities with EPSS and CISA KEV enrichment. These tools solve different problems — here's when to use each, and when to use both.
Free Dependency Scanning Tools 2026 Guide
You don't need an enterprise budget to scan dependencies for vulnerabilities. This is the broadest survey: 7 free tools across every major language, including hosted options like GeekWala, Dependabot, and Trivy alongside CLI-native scanners.
Trivy Container Scan vs EPSS Enrichment
Trivy is a broad infrastructure scanner covering containers, Kubernetes, and IaC. GeekWala is a focused dependency scanner enriching every finding with EPSS exploit probability and CISA KEV status. Here's how the two tools actually detect and prioritize differently.