Comparison Articles
All GeekWala articles in the Comparison category.
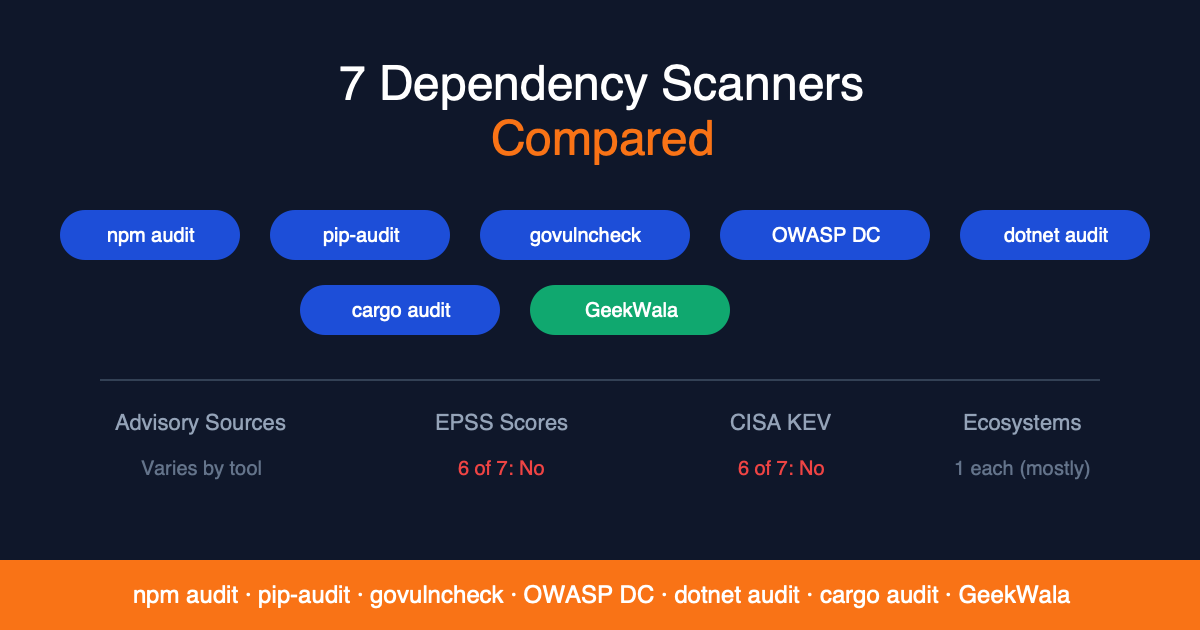
5 Ecosystem-Native Dependency Scanners Compared
Every ecosystem has a built-in vulnerability scanner. None of them tell you which CVEs are being exploited right now. We compared 5 ecosystem-native CLI scanners across advisory sources, exploitation signals, ecosystem coverage, and pricing.
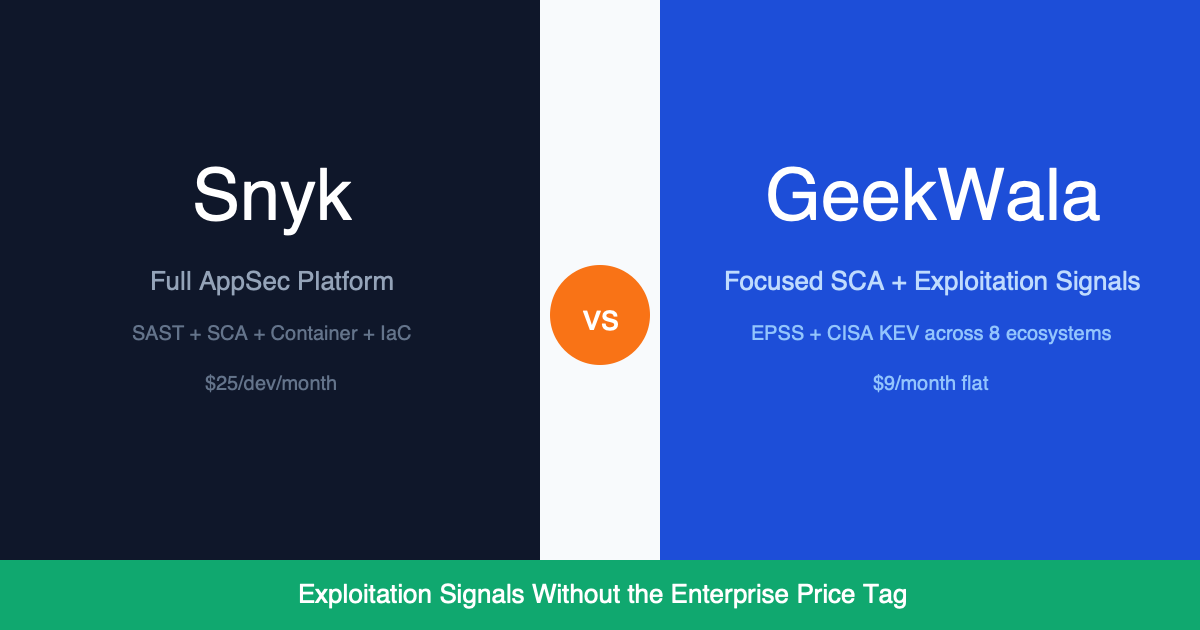
Snyk vs GeekWala: Priority Score vs EPSS + KEV
Snyk's composite scoring (Risk Score, or Priority Score by default) and GeekWala's separate EPSS + CISA KEV fields both aim to cut through CVSS-only alert fatigue, but they get there differently. Here's how each tool's data sources, scan triggers, and prioritization signals actually work.

npm audit's CVSS Scores vs EPSS Triage
npm audit labels every CVE by CVSS-based severity, but CVSS alone is a poor predictor of real exploitation. Learn how EPSS and CISA KEV signals cut through alert fatigue and prioritize the vulnerabilities that actually matter.