Workflow Articles
All GeekWala articles in the Workflow category.
Dependency Scanning in GitLab CI and Jenkins
GitLab's built-in dependency scanning is locked behind the Ultimate tier. This guide shows how to build the same PR-gate-plus-scheduled-scan pattern in .gitlab-ci.yml and Jenkinsfile using OSV-Scanner — no license upgrade required.
Add a Dependency Security Badge to Your README
A live badge answers the security question before anyone asks it. Generate your GeekWala badge, embed it with Markdown, HTML, or reStructuredText, and every view links back to a public scan page — no outreach required.
Import a GitHub Repo for Dependency Scanning
Manual manifest uploads work for a one-off check, but a repo-connected project is easy to re-sync and re-scan as new dependencies and new CVEs arrive. Here's the exact GitHub import flow, the permissions it requests, and what to do when it fails.
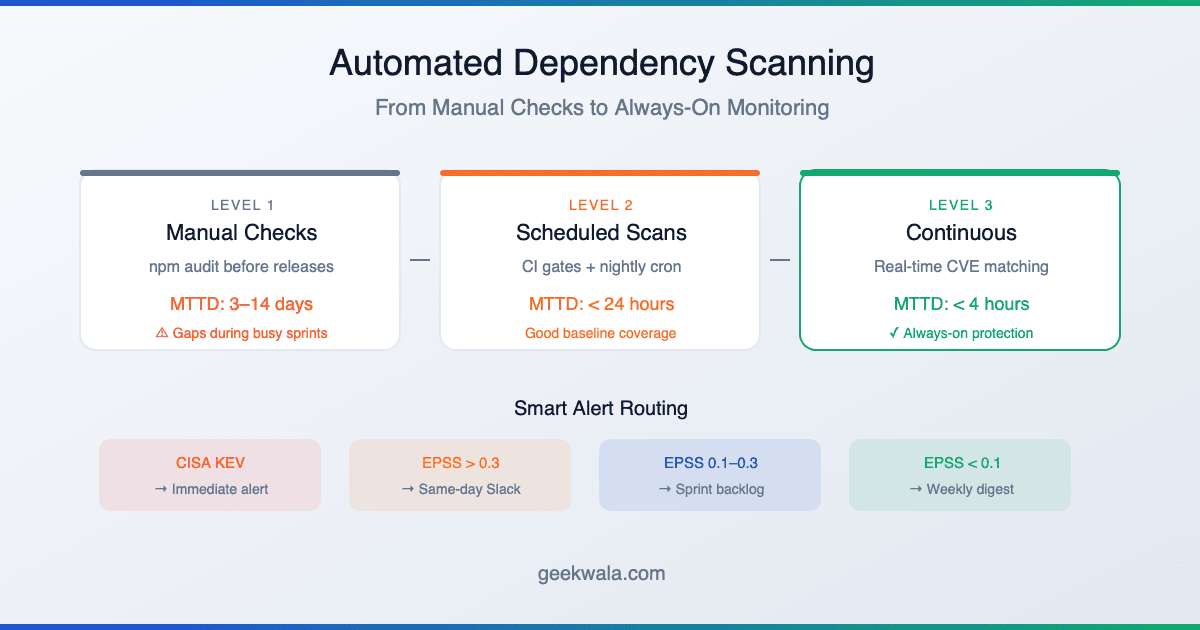
Automated Dependency Scanning: How It Works
A CVE drops Tuesday, your scan runs Friday. Three days of exposure. Learn how to set up automated dependency scanning with scheduled scans, smart alert routing via EPSS, and webhook notifications when each scan completes.
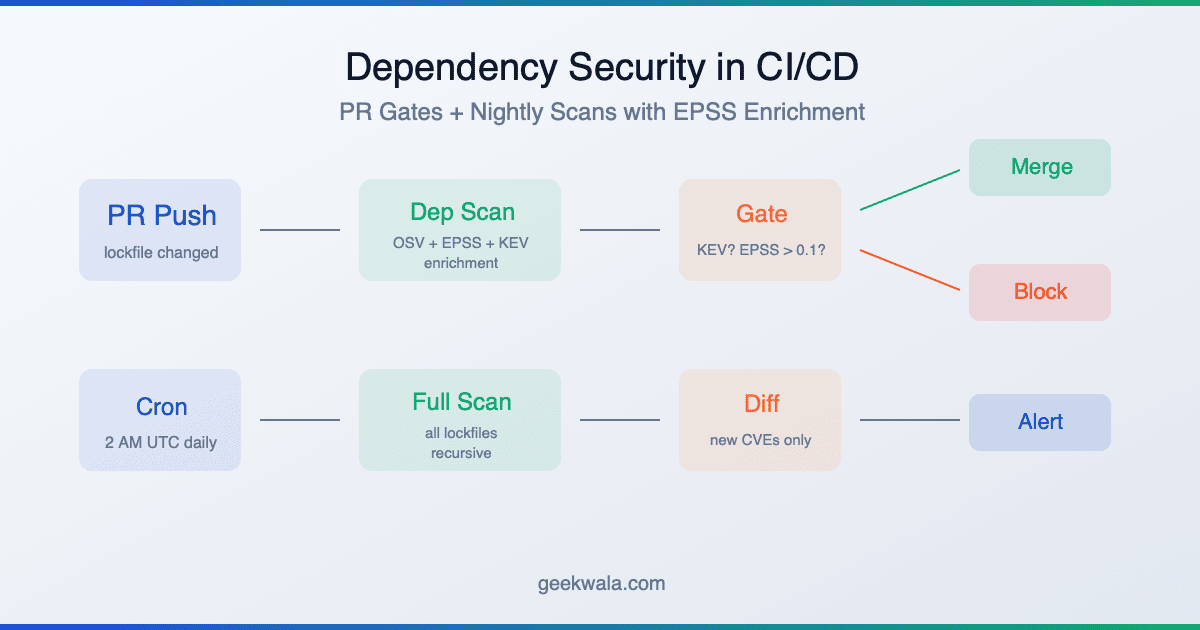
Dependency Scanning in GitHub Actions
Your CI/CD pipeline checks code quality but not dependency security. This guide shows exact GitHub Actions YAML configs for PR vulnerability gates and scheduled nightly scans — with EPSS enrichment to cut false positives.