Articles Tagged SCA
All GeekWala articles tagged SCA.
Dependency License Compliance Guide
License compliance is the other reason organizations buy SCA, alongside vulnerabilities. This guide covers permissive vs copyleft licenses, the AGPL network clause every SaaS team should know, and how to audit what your dependency tree actually licenses you to do.
Software Composition Analysis Tools (2026)
Software composition analysis buyers evaluate a shortlist, not a single product. Here's a neutral, sourced comparison of 10 SCA tools — vulnerability detection, license compliance, and reachability — including where GeekWala fits and where it doesn't.
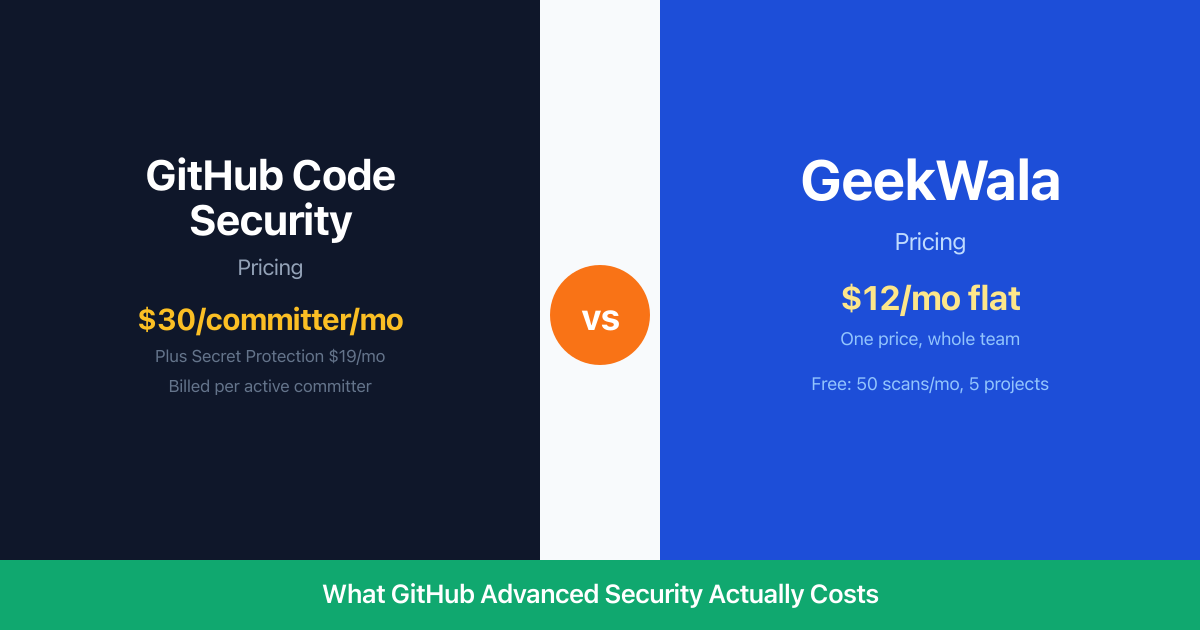
GitHub Code Security Pricing Explained
GitHub split Advanced Security into two per-committer SKUs. Here's what Code Security and Secret Protection actually cost at real team sizes, and how GeekWala's flat pricing compares for dependency scanning specifically.
Trivy vs Grype: Open-Source Scanner Comparison
Trivy (Aqua Security) and Grype (Anchore) are the two most-adopted open-source vulnerability scanners for containers and dependencies. Here's how they actually differ — no vendor picked.
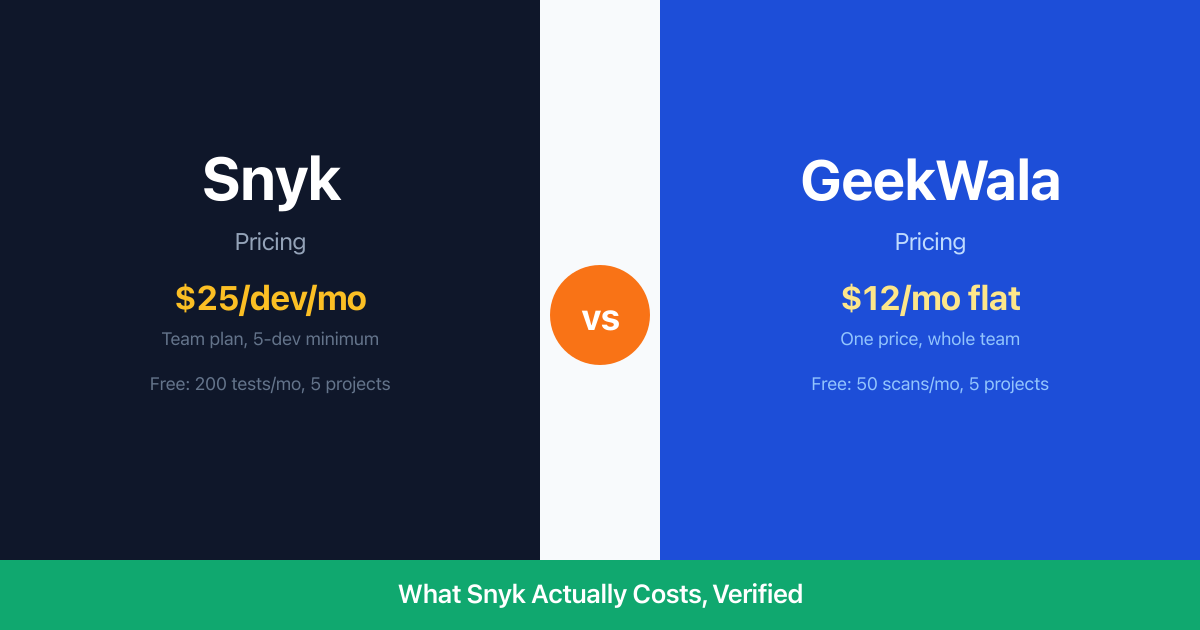
Snyk Pricing Explained: What It Costs vs GeekWala
Snyk's pricing page lists four tiers and a per-developer model that gets expensive fast. Here's what Snyk actually costs at real team sizes, the free-tier limit teams hit first, and how GeekWala's flat pricing compares.
Snyk vs Dependabot vs Trivy: SCA Compared
We put Snyk, Dependabot, and Trivy through the same 10-point checklist without a vendor holding the pen. One wins on breadth, one wins on cost, one wins on zero setup — none wins everything.
Mend vs Flat-Rate EPSS + KEV Scanning
Mend bundles SCA, container, and license-compliance scanning with per-developer, contact-sales pricing built for large security teams. GeekWala is flat-rate dependency scanning with EPSS and CISA KEV on every finding. Here's an honest, feature-by-feature comparison.