Security Articles
All GeekWala articles in the Security category.
200 Dependabot Alerts: Which 3 to Fix Today
The average GitHub repository has 67 open Dependabot alerts. Most developers either ignore them all or waste time on low-risk CVEs. The 3-Signal Triage Method — combining CVSS with EPSS and CISA KEV — cuts your actionable list from hundreds to single digits, so you fix what actually matters.
CVSS, EPSS, KEV, SSVC, and LEV Compared
Five vulnerability scoring systems compete for developer attention: CVSS, EPSS, CISA KEV, SSVC, and LEV. Each answers a different question about risk. This guide compares all five — what they measure, who maintains them, and how to combine the right signals for your team.
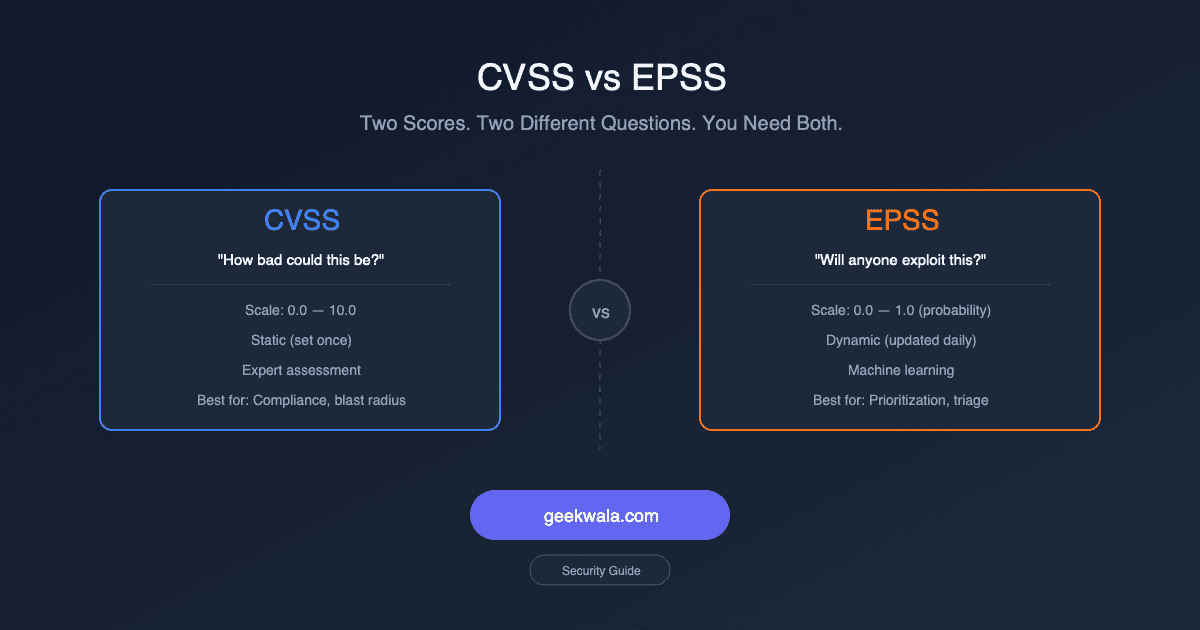
CVSS vs EPSS: Two Vulnerability Score Systems
CVSS and EPSS both score vulnerabilities, but they answer different questions. CVSS asks 'how bad could this be?' while EPSS asks 'will anyone exploit this?' This comparison shows where they agree, where they diverge, and why you need both.
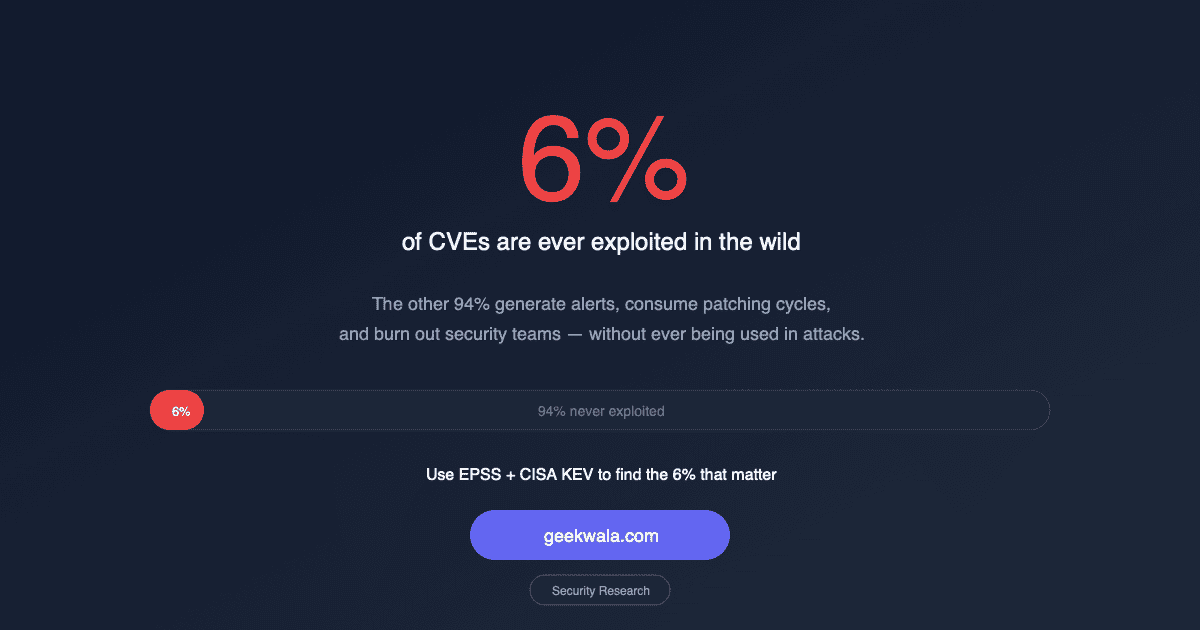
At Most 6% of CVEs Are Exploited: What It Means
At most ~6% of published CVEs are ever exploited in the wild — the most generous estimate, with stricter datasets nearer 1-2%. The rest generate alerts and burn out security teams without ever being used in attacks. This has profound implications for vulnerability prioritization.
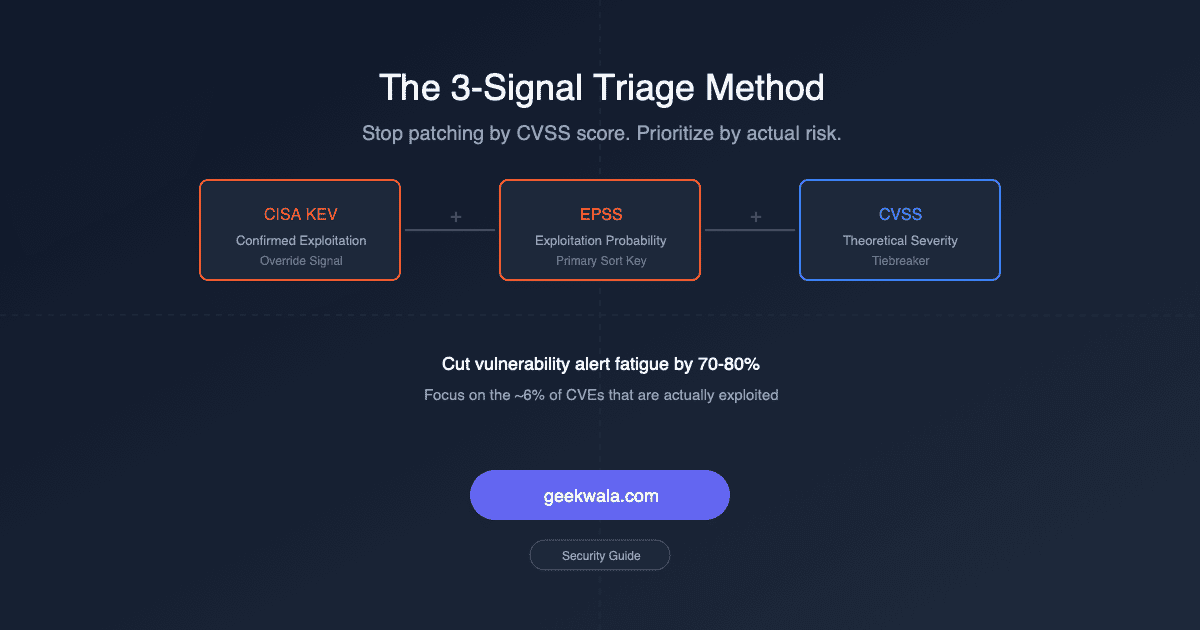
Vulnerability Prioritization: 3-Signal Triage
Most teams waste 80% of their patching effort on vulnerabilities nobody is exploiting. The 3-Signal Triage Method combines CVSS severity, EPSS exploitation probability, and CISA KEV status into a repeatable framework that cuts noise and focuses your team on real risk.
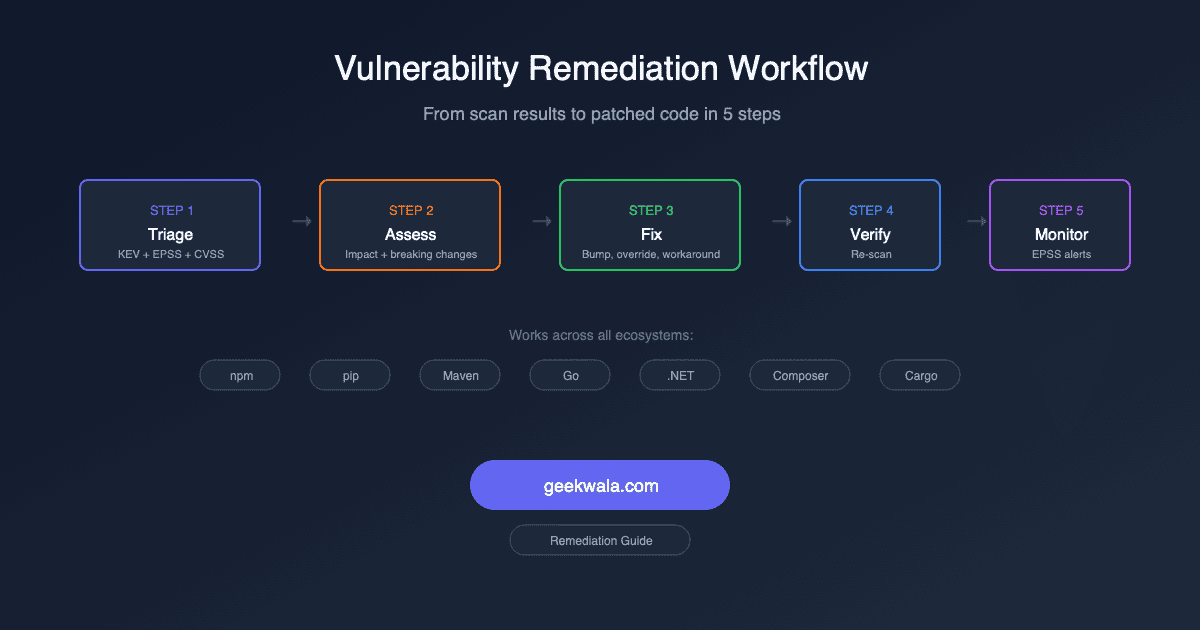
Vulnerability Remediation: Scan to Patched Code
Finding vulnerabilities is easy. Fixing them without breaking your app is where teams stall. This 5-step workflow covers triage, impact assessment, ecosystem-specific fix strategies, verification, and monitoring.
What is EPSS? Exploit Prediction Scoring
The Exploit Prediction Scoring System (EPSS) estimates the probability a CVE will be exploited in the wild within 30 days. Learn how to read EPSS scores, combine them with CVSS, and build a triage workflow that actually reduces risk.
CISA KEV: Actively Exploited Vulnerabilities
CISA maintains the Known Exploited Vulnerabilities catalog — a curated list of CVEs actively being used in attacks right now. If a vulnerability is on KEV, it is not theoretical. Learn what KEV is, how entries are added, and how to use it in your triage workflow.