Articles Tagged EU CRA
All GeekWala articles tagged EU CRA.
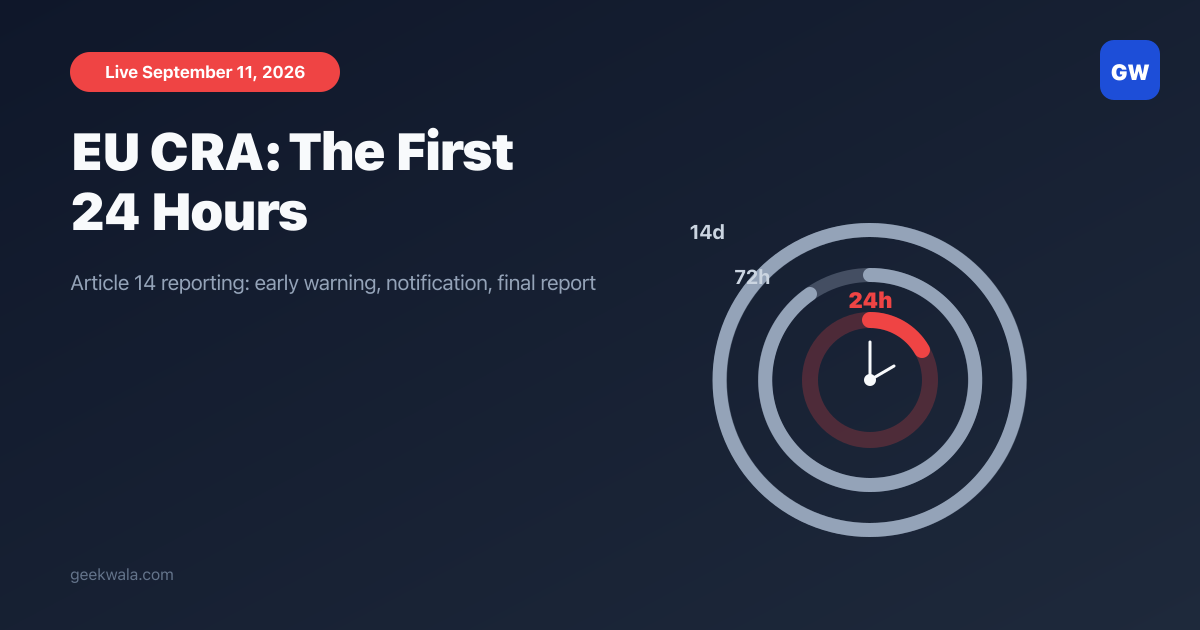
EU CRA Day One: Your First 24 Hours
Most CRA coverage is written for the person deciding whether the regulation applies. This is for the engineer who gets paged at 09:14 with 24 hours on the clock: the three deadlines, a ready-to-use early-warning template, and the mistakes that blow the window.
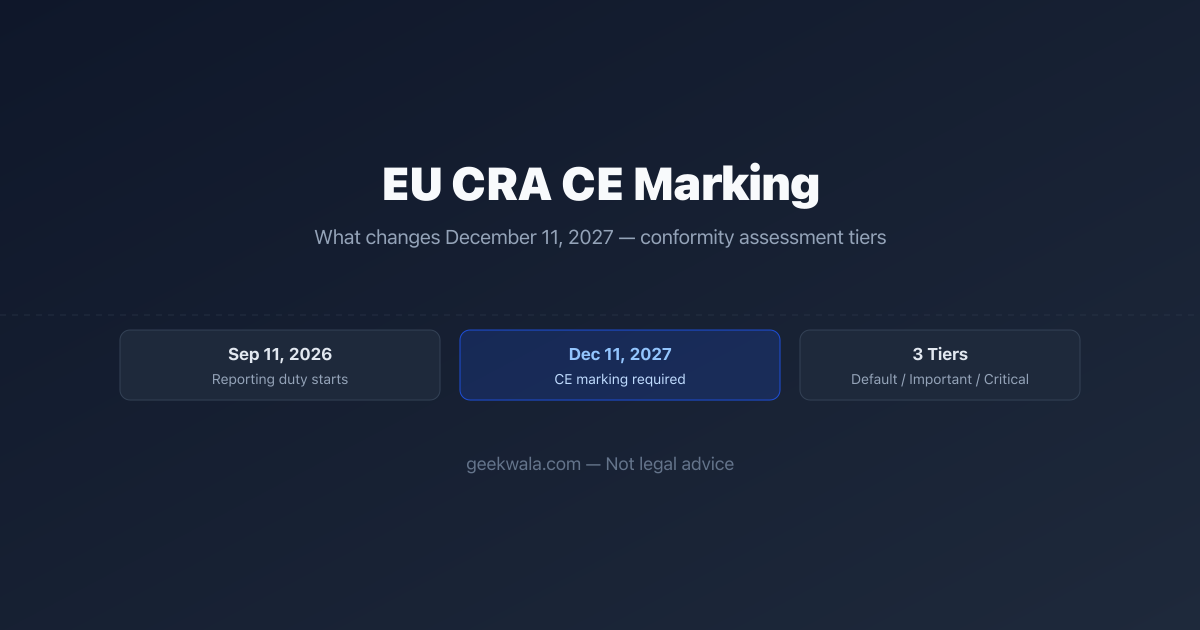
EU CRA CE Marking: The December 11, 2027 Deadline
September 2026 is the CRA's reporting deadline. December 11, 2027 is the bigger one: mandatory CE marking, essential cybersecurity requirements, and formal conformity assessment for every in-scope product. What changes, which tier your product falls into, and how to prepare.
EU CRA Reporting Obligations: Article 14 Now in Force
Most EU Cyber Resilience Act coverage points at the December 2027 deadline. The obligation that landed first — 24-hour reporting of actively exploited vulnerabilities — has applied since September 11, 2026. Here's how the reporting regime works and who it applies to.
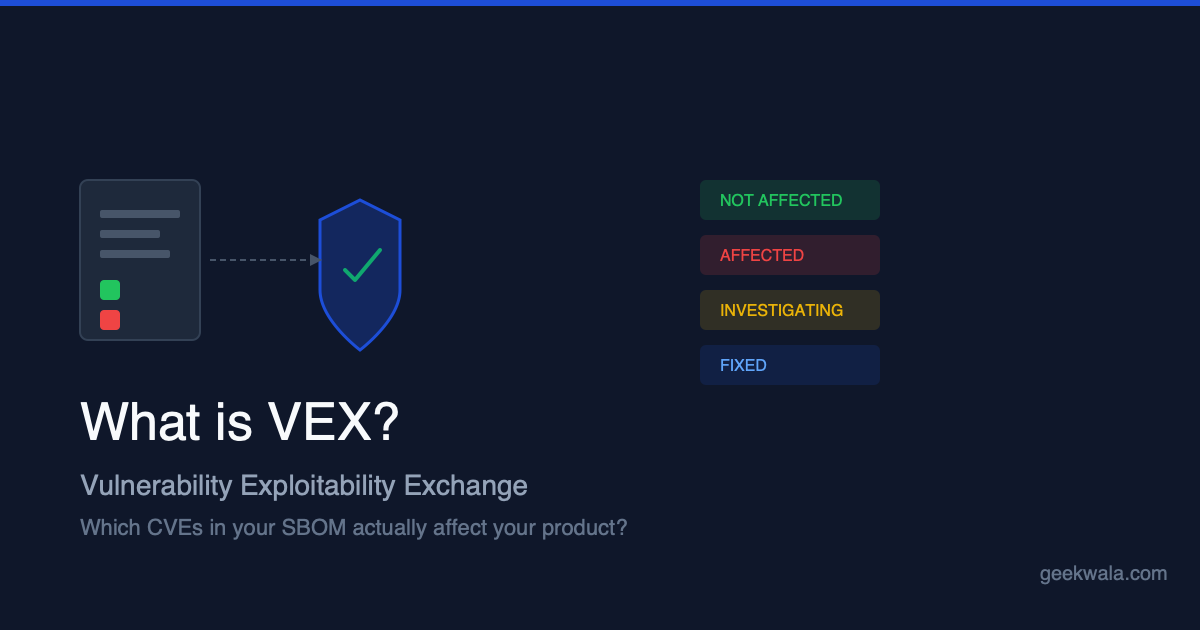
What Is VEX? Vulnerability Exploitability
Your SBOM says you use a vulnerable package. But does the vulnerability actually affect your product? VEX answers that question with a machine-readable document that states whether a known CVE is exploitable, not affected, under investigation, or fixed in your specific product.
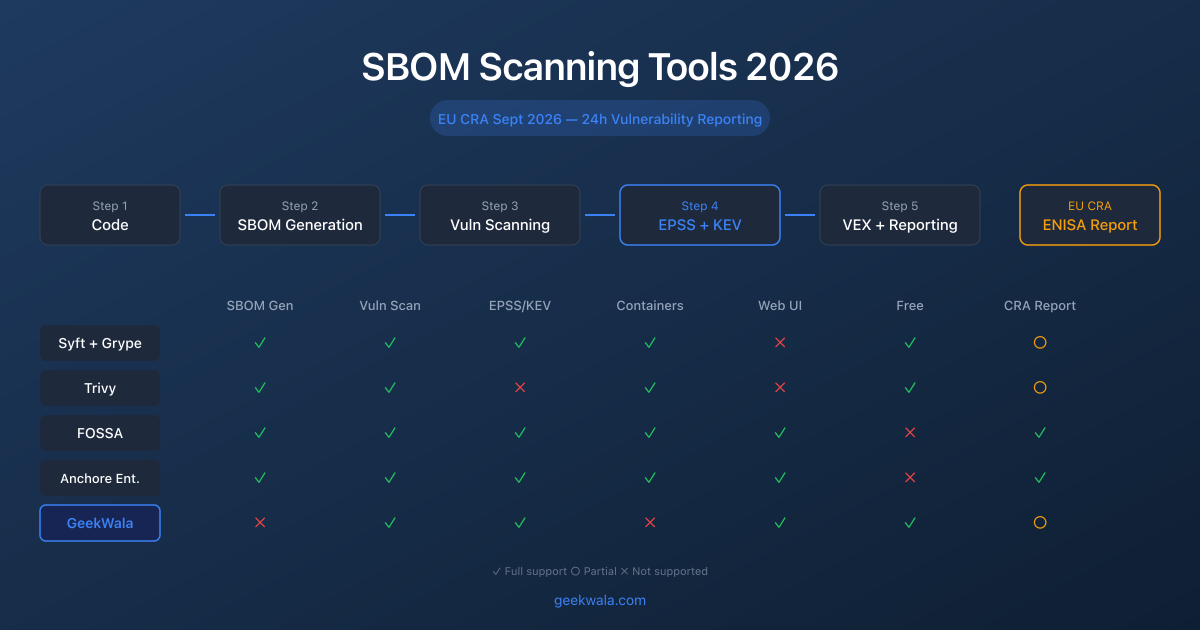
SBOM Scanning Tools 2026: EU CRA Guide
EU CRA's September 2026 deadline requires 24-hour reporting of actively exploited vulnerabilities. You can't meet that deadline without SBOM tooling. This guide covers which tools generate and scan SBOMs, handle EU CRA workflows, and fit your team size and budget.
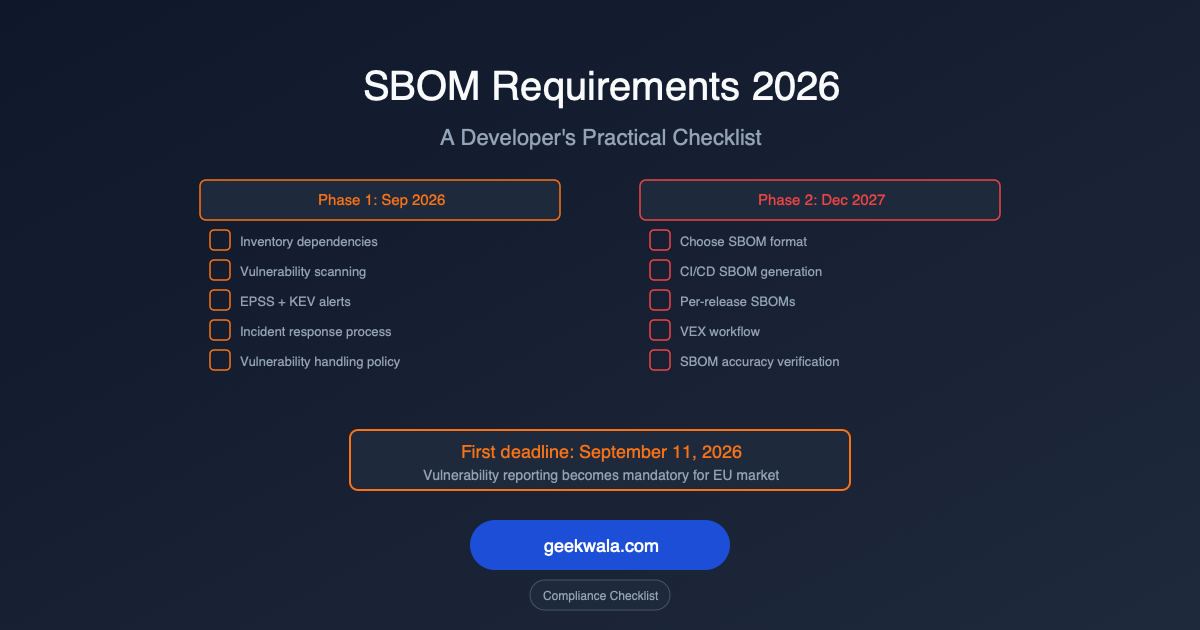
SBOM Requirements 2026: Developer Checklist
The EU CRA vulnerability reporting deadline is September 2026. Here's the checklist your team needs to be ready — organized into two phases with specific action items for each.
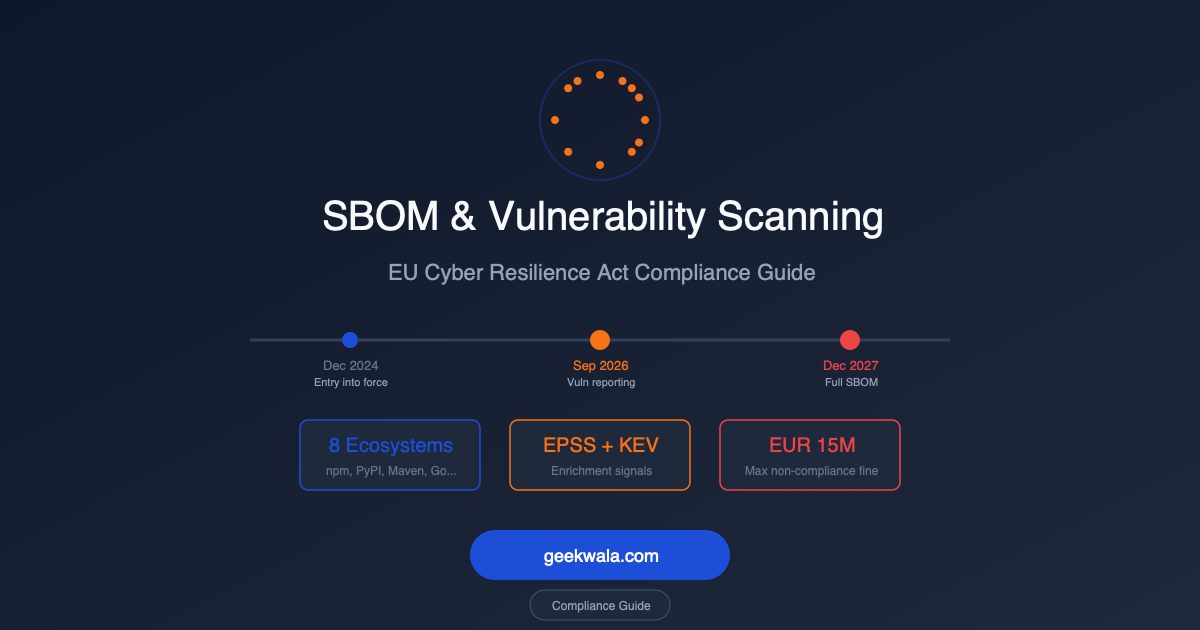
SBOM Scanning and the EU Cyber Resilience Act
Starting September 2026, the EU Cyber Resilience Act requires vulnerability and incident reporting for software sold in Europe. By December 2027, you'll need a machine-readable Software Bill of Materials. If your software has open-source dependencies — and it does — this directly affects you.