Articles Tagged CISA KEV
All GeekWala articles tagged CISA KEV.
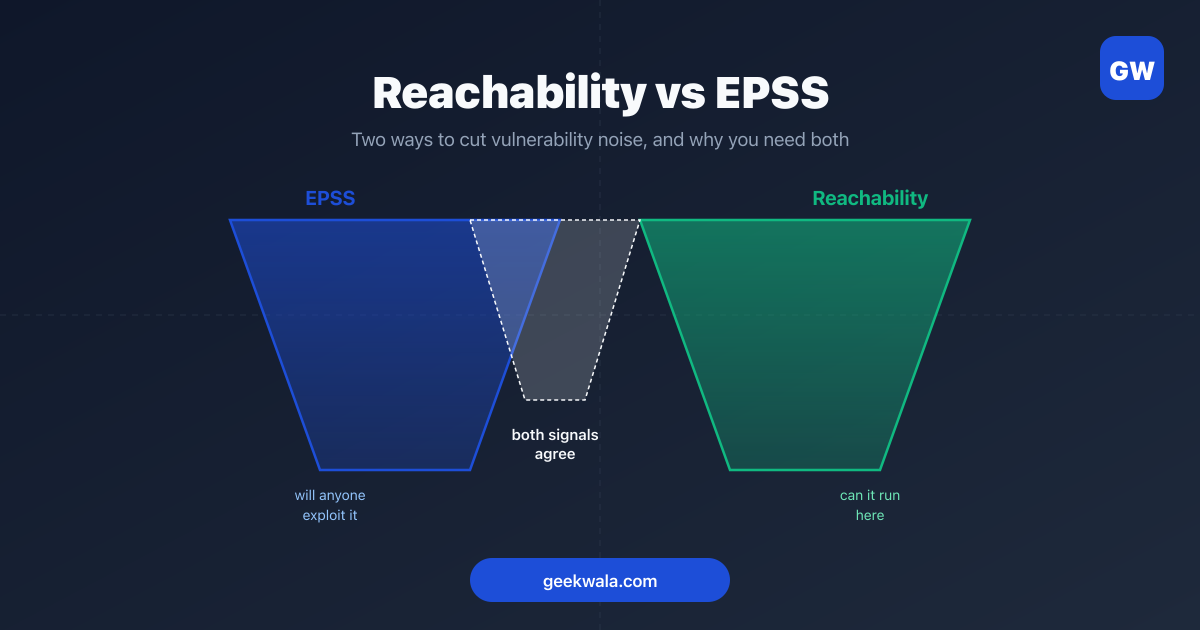
Reachability vs EPSS: Cutting False Positives
Two scanners, same repo, two different finding counts. Neither is wrong. Reachability asks whether your code calls the vulnerable function. EPSS asks whether anyone will exploit it. How they compare, where each fails, and how to combine them without discarding the KEV signal that matters most.
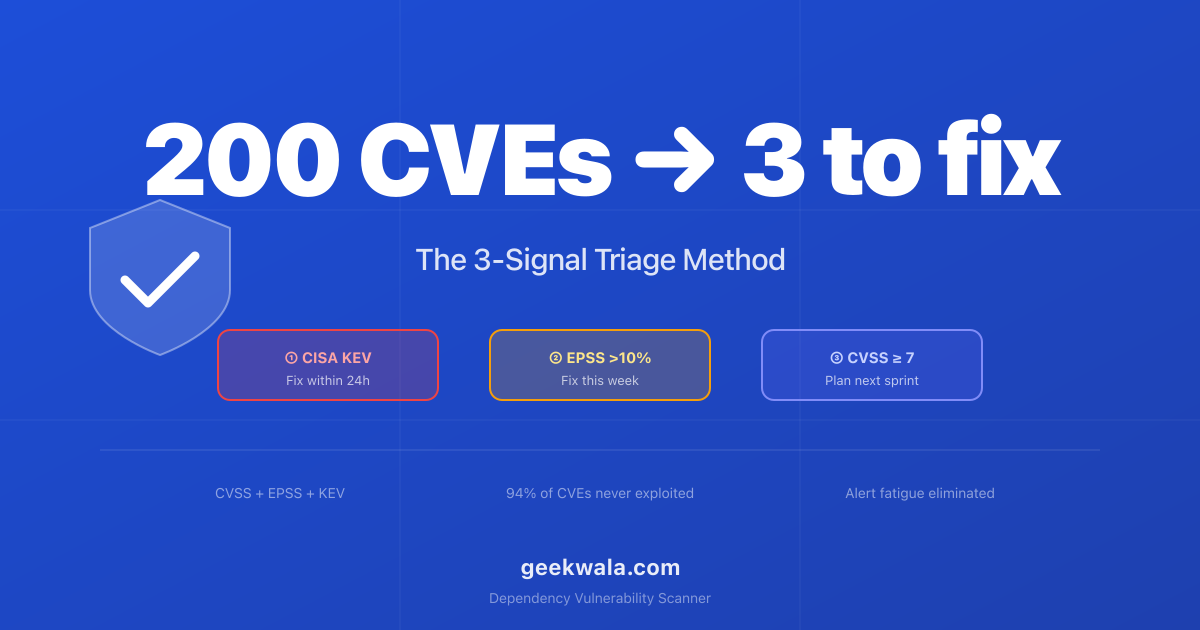
Your Scanner Found 200 CVEs: What to Do
Alert fatigue is the #1 reason teams ignore vulnerability scanners. A developer opens the dashboard, sees 200 red CVEs, and closes the tab. This article is the actionable playbook that turns 200 alerts into a 3-item "fix today" list using the 3-Signal Triage Method (CVSS + EPSS + KEV).
200 Dependabot Alerts: Which 3 to Fix Today
The average GitHub repository has 67 open Dependabot alerts. Most developers either ignore them all or waste time on low-risk CVEs. The 3-Signal Triage Method — combining CVSS with EPSS and CISA KEV — cuts your actionable list from hundreds to single digits, so you fix what actually matters.
CVSS, EPSS, KEV, SSVC, and LEV Compared
Five vulnerability scoring systems compete for developer attention: CVSS, EPSS, CISA KEV, SSVC, and LEV. Each answers a different question about risk. This guide compares all five — what they measure, who maintains them, and how to combine the right signals for your team.
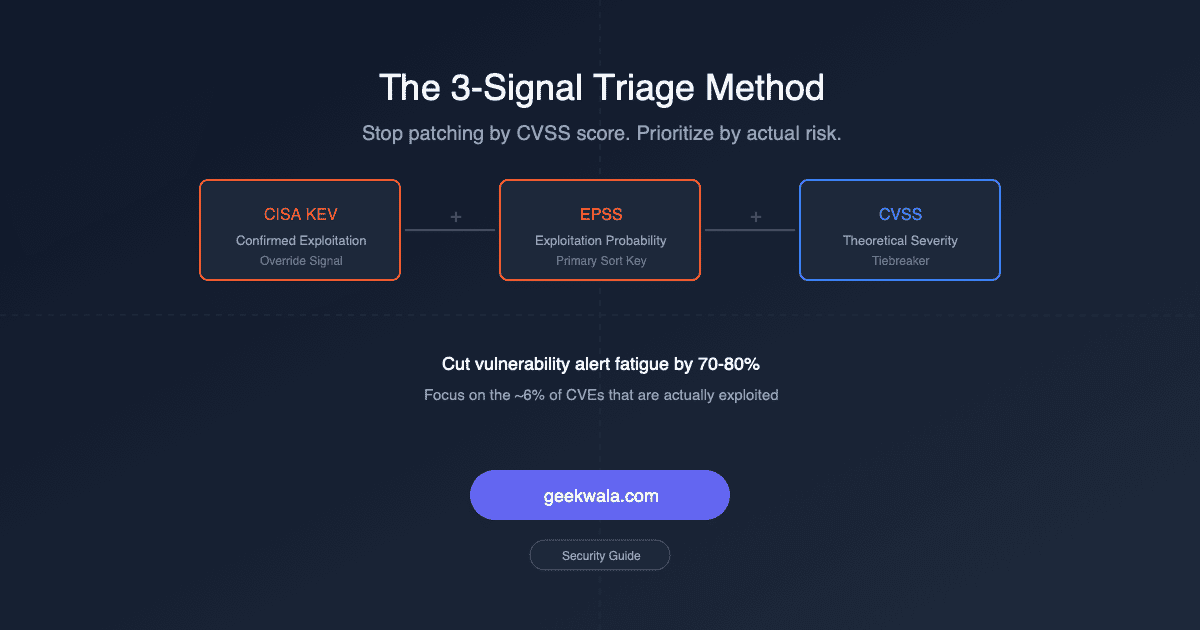
Vulnerability Prioritization: 3-Signal Triage
Most teams waste 80% of their patching effort on vulnerabilities nobody is exploiting. The 3-Signal Triage Method combines CVSS severity, EPSS exploitation probability, and CISA KEV status into a repeatable framework that cuts noise and focuses your team on real risk.